Update passive_journal_centralization_guide_self_signed_certs.md
Costa Tsaousis committed
Oct 18, 2023 at 20:00 UTC
ec6a0614908f2f124cbafd3bd4d2a027a83f4d0b
1 file changed
+13
-4
collectors/systemd-journal.plugin/passive_journal_centralization_guide_self_signed_certs.md
+13
-4
@@ -2,7 +2,7 @@
2
3
This page will guide you through creating a **passive** journal centralization setup using **self-signed certificates** for encryption and authorization.
4
5
-Once you centralize your infrastructure logs to a server, Netdata will automatically detect all the logs from all servers and organize them in sources. With the setup described in this document, Netdata will automatically name all remote sources using the names of the clients, as they are described at their certificates.
5
+Once you centralize your infrastructure logs to a server, Netdata will automatically detect all the logs from all servers and organize them in sources. With the setup described in this document, on recent systemd versions, Netdata will automatically name all remote sources using the names of the clients, as they are described at their certificates (on older versions, the names will be IPs or reverse DNS lookups of the IPs).
6
7
A **passive** journal server waits for clients to push their metrics to it, so in this setup we will:
8
@@ -46,9 +46,9 @@ sudo ./systemd-journal-self-signed-certs.sh "server1" "DNS:hostname1" "IP:10.0.0
46
47
Where:
48
49
- - `server1` is the canonical name of the server. This is how this server will be identified by `systemd-journal-remote` and Netdata when you view the logs on the dashboard.
49
+ - `server1` is the canonical name of the server. On newer systemd version, this name will be used by `systemd-journal-remote` and Netdata when you view the logs on the dashboard.
50
- `DNS:hostname1` is a DNS name that the server is reachable at. Add `"DNS:xyz"` multiple times to define multiple DNS names for the server.
51
- - `IP:1.2.3.4` is an IP that the server is reachable at. Add `"IP:xyz"` multiple times to define multiple IPs for the server.
51
+ - `IP:10.0.0.1` is an IP that the server is reachable at. Add `"IP:xyz"` multiple times to define multiple IPs for the server.
52
53
Repeat this process to create the certificates for all your servers. You can add servers as required, at any time in the future.
54
@@ -112,9 +112,14 @@ and add the following lines into the instructed place, and choose your desired p
112
ListenStream=<DESIRED_PORT>
113
```
114
115
-Assuming that you have already copied the `runme-on-XXX.sh` script on the server, run this:
115
+Next, run the `runme-on-XXX.sh` script on the server:
116
117
```bash
118
+# if you run the certificate authority on the server:
119
+sudo /etc/ssl/systemd-journal/runme-on-XXX.sh
120
+
121
+# if you run the certificate authority elsewhere,
122
+# assuming you have coped the runme-on-XXX.sh script (as described above):
123
sudo bash /tmp/runme-on-XXX.sh
124
```
125
@@ -130,6 +135,8 @@ sudo systemctl enable systemd-journal-remote.service
135
136
`systemd-journal-remote` is now listening for incoming journals from remote hosts.
137
138
+> Remember to delete `/tmp/runme-on-XXX.sh` to make sure your certificates are secure.
139
+
140
## Client configuration
141
142
On the clients, install `systemd-journal-remote` (it includes `systemd-journal-upload`):
@@ -183,6 +190,8 @@ sudo systemctl restart systemd-journal-upload.service
190
191
The client should now be pushing logs to the central server.
192
193
+> Remember to delete `/tmp/runme-on-XXX.sh` to make sure your certificates are secure.
194
+
195
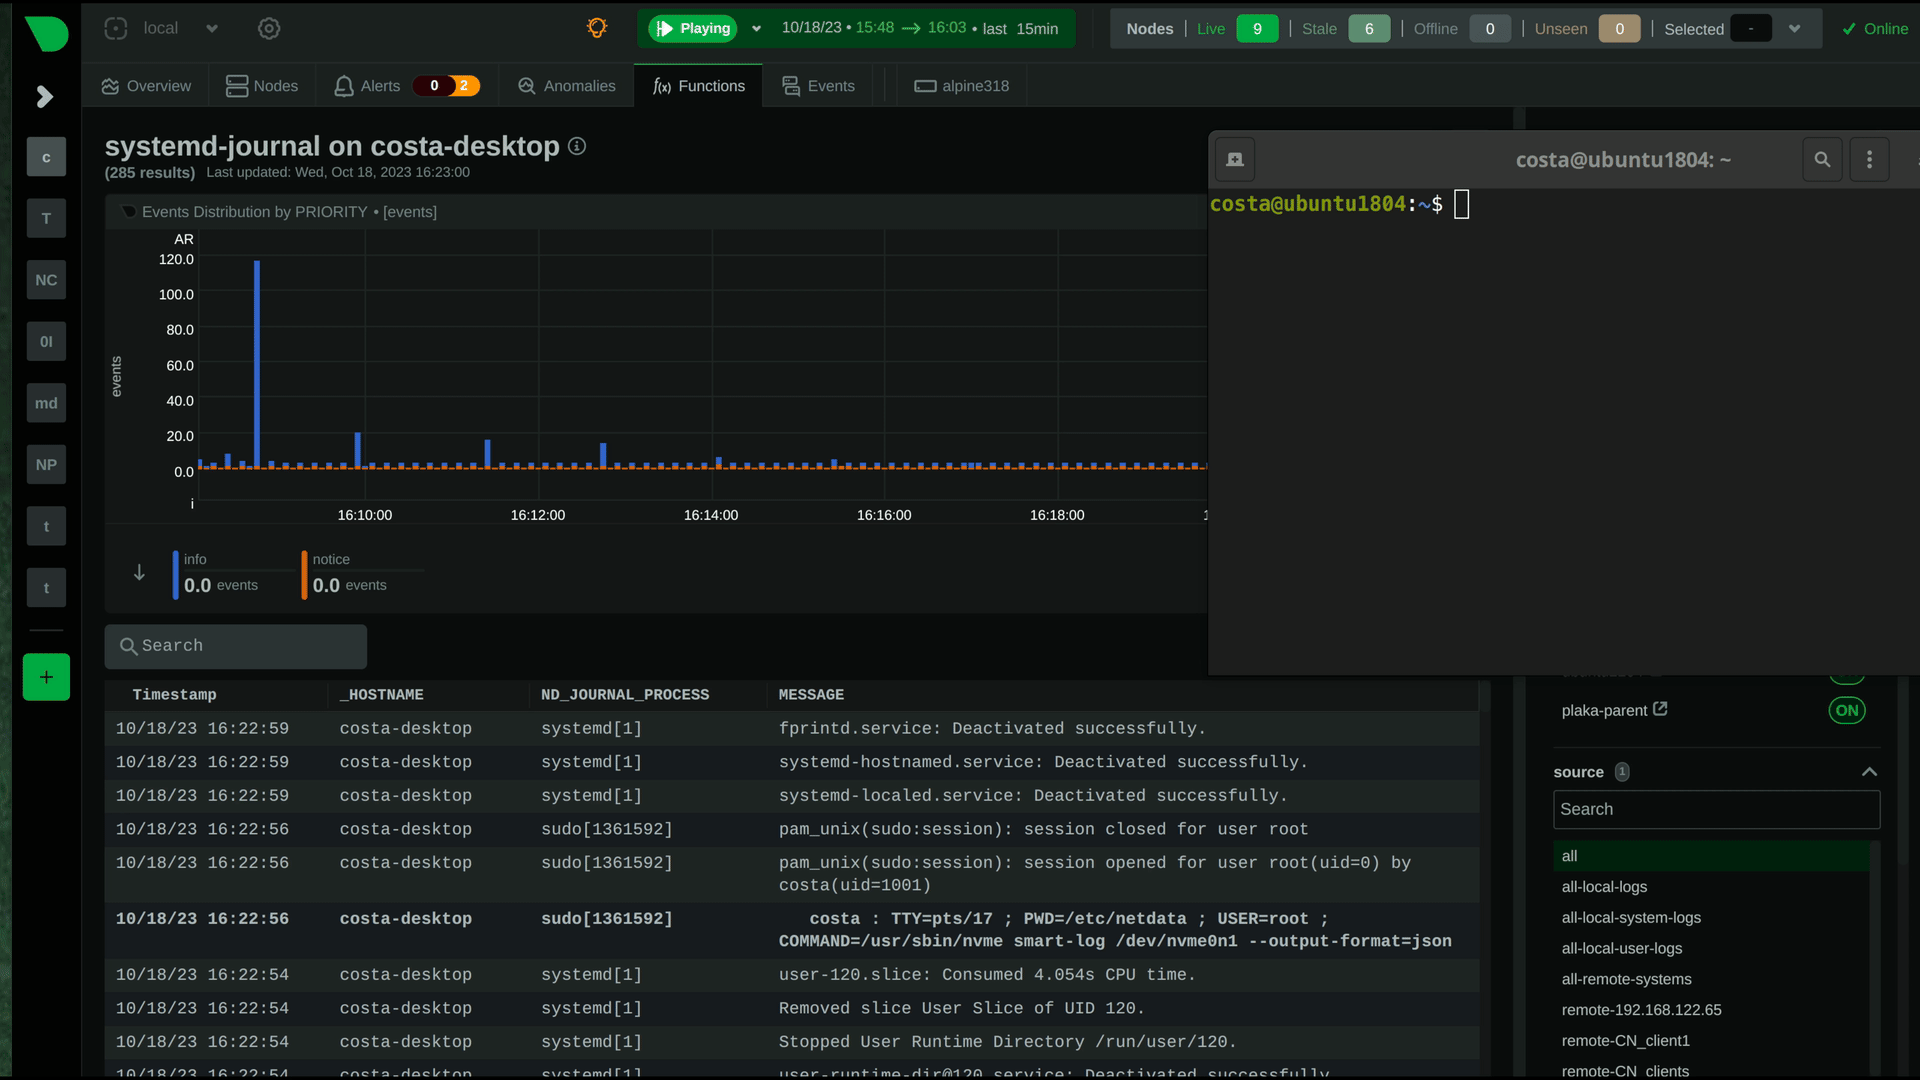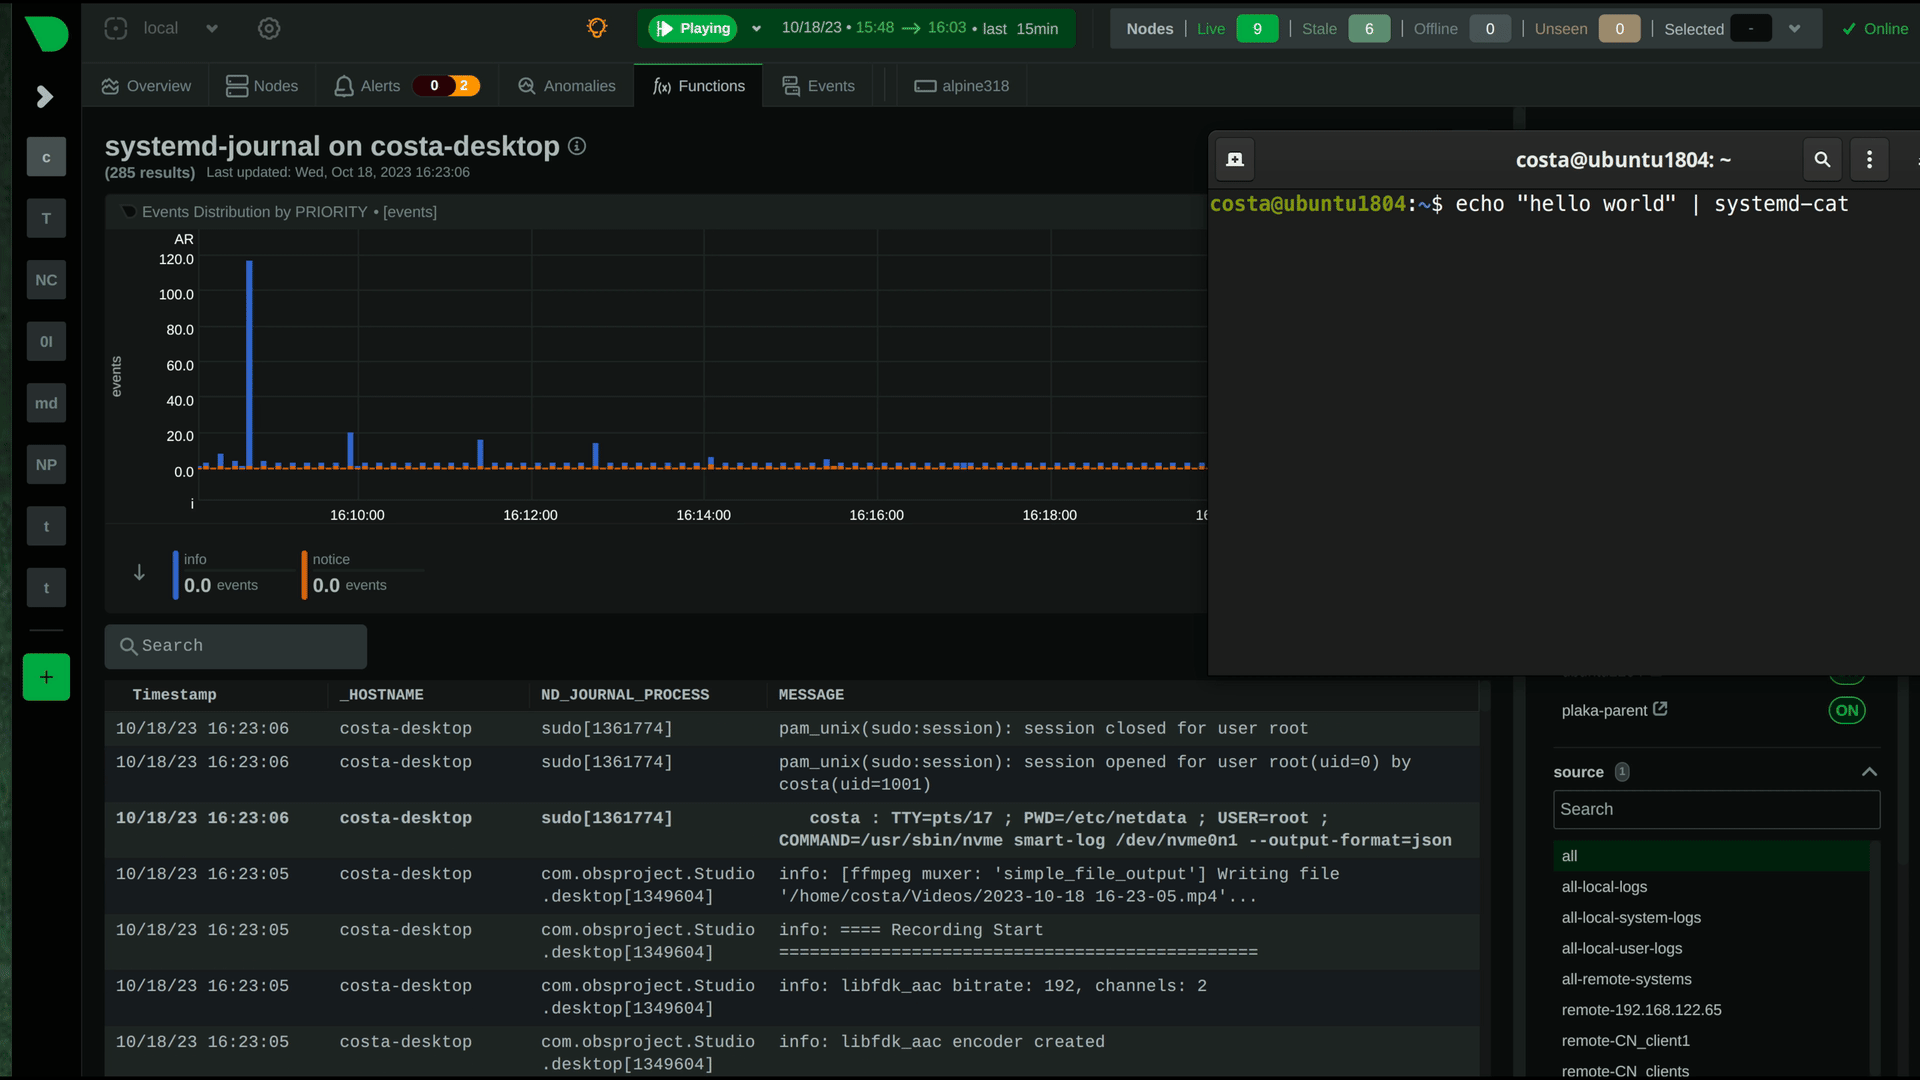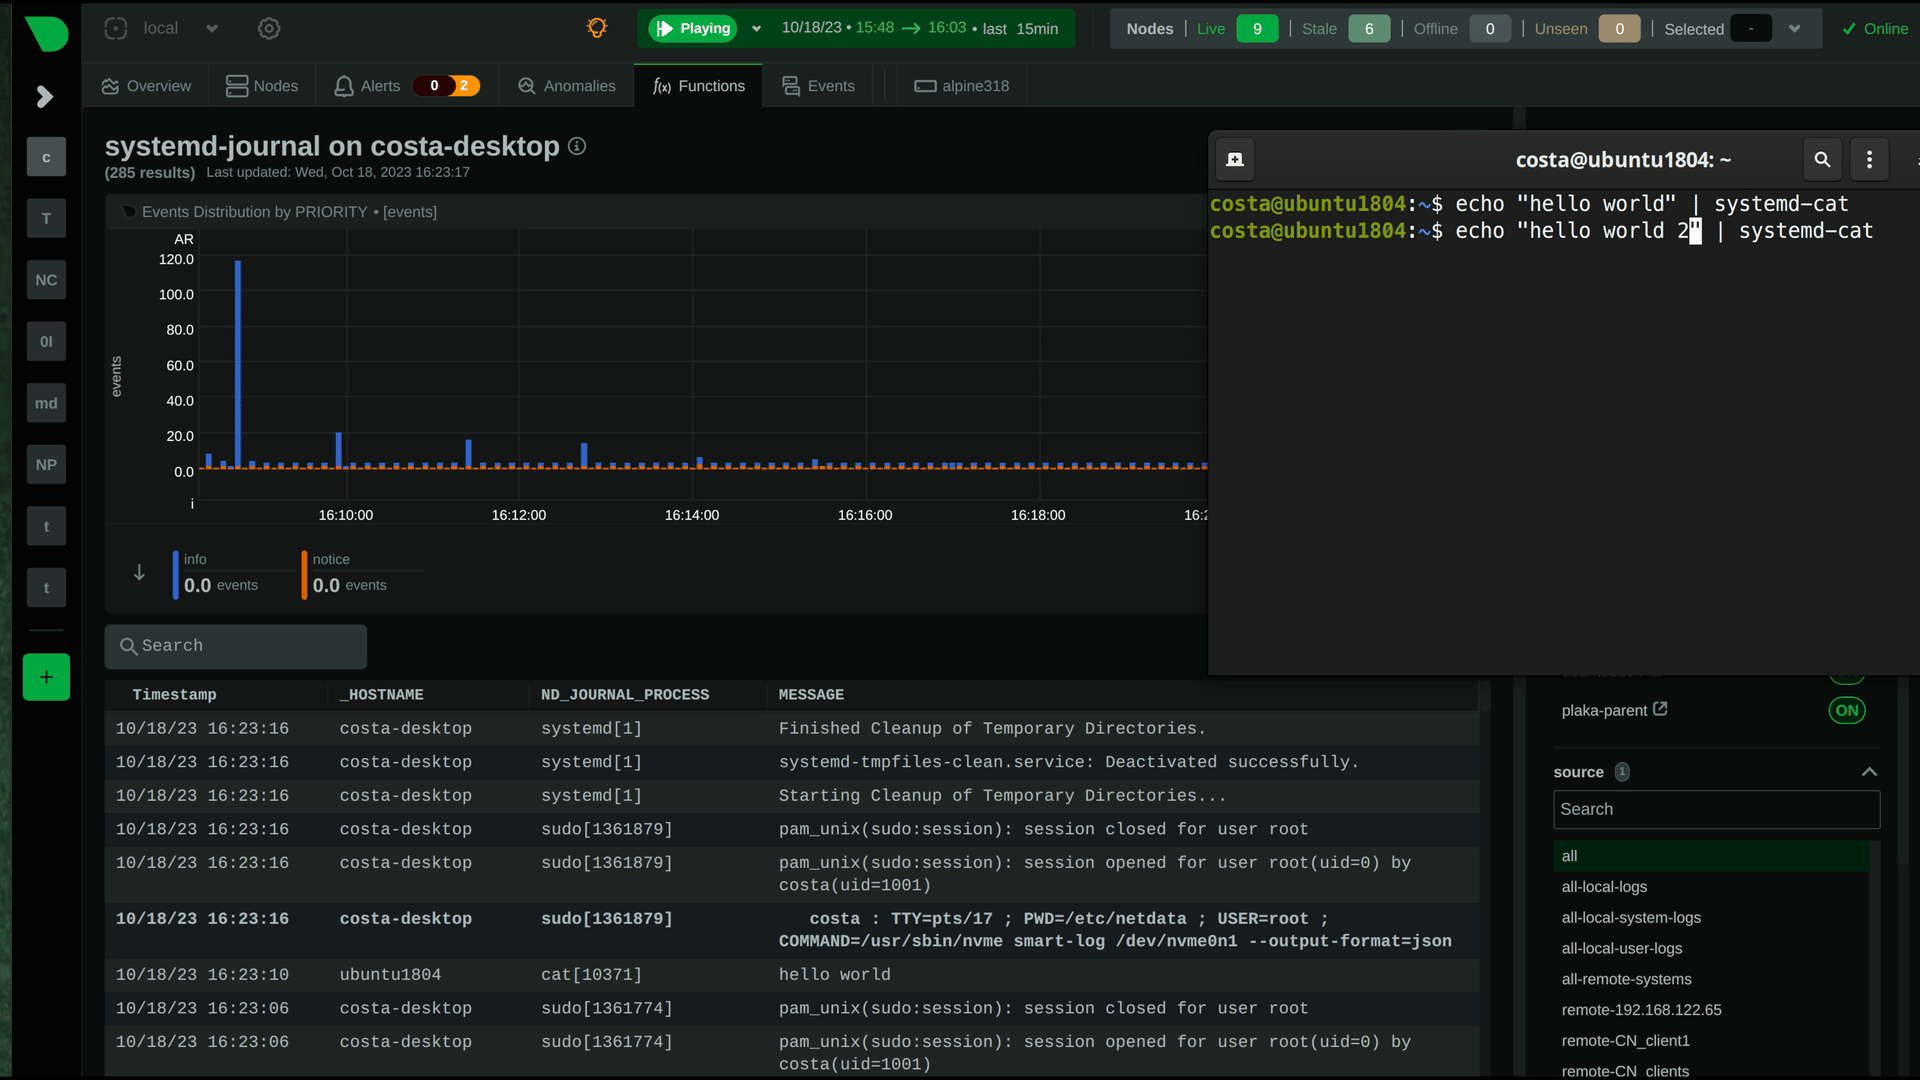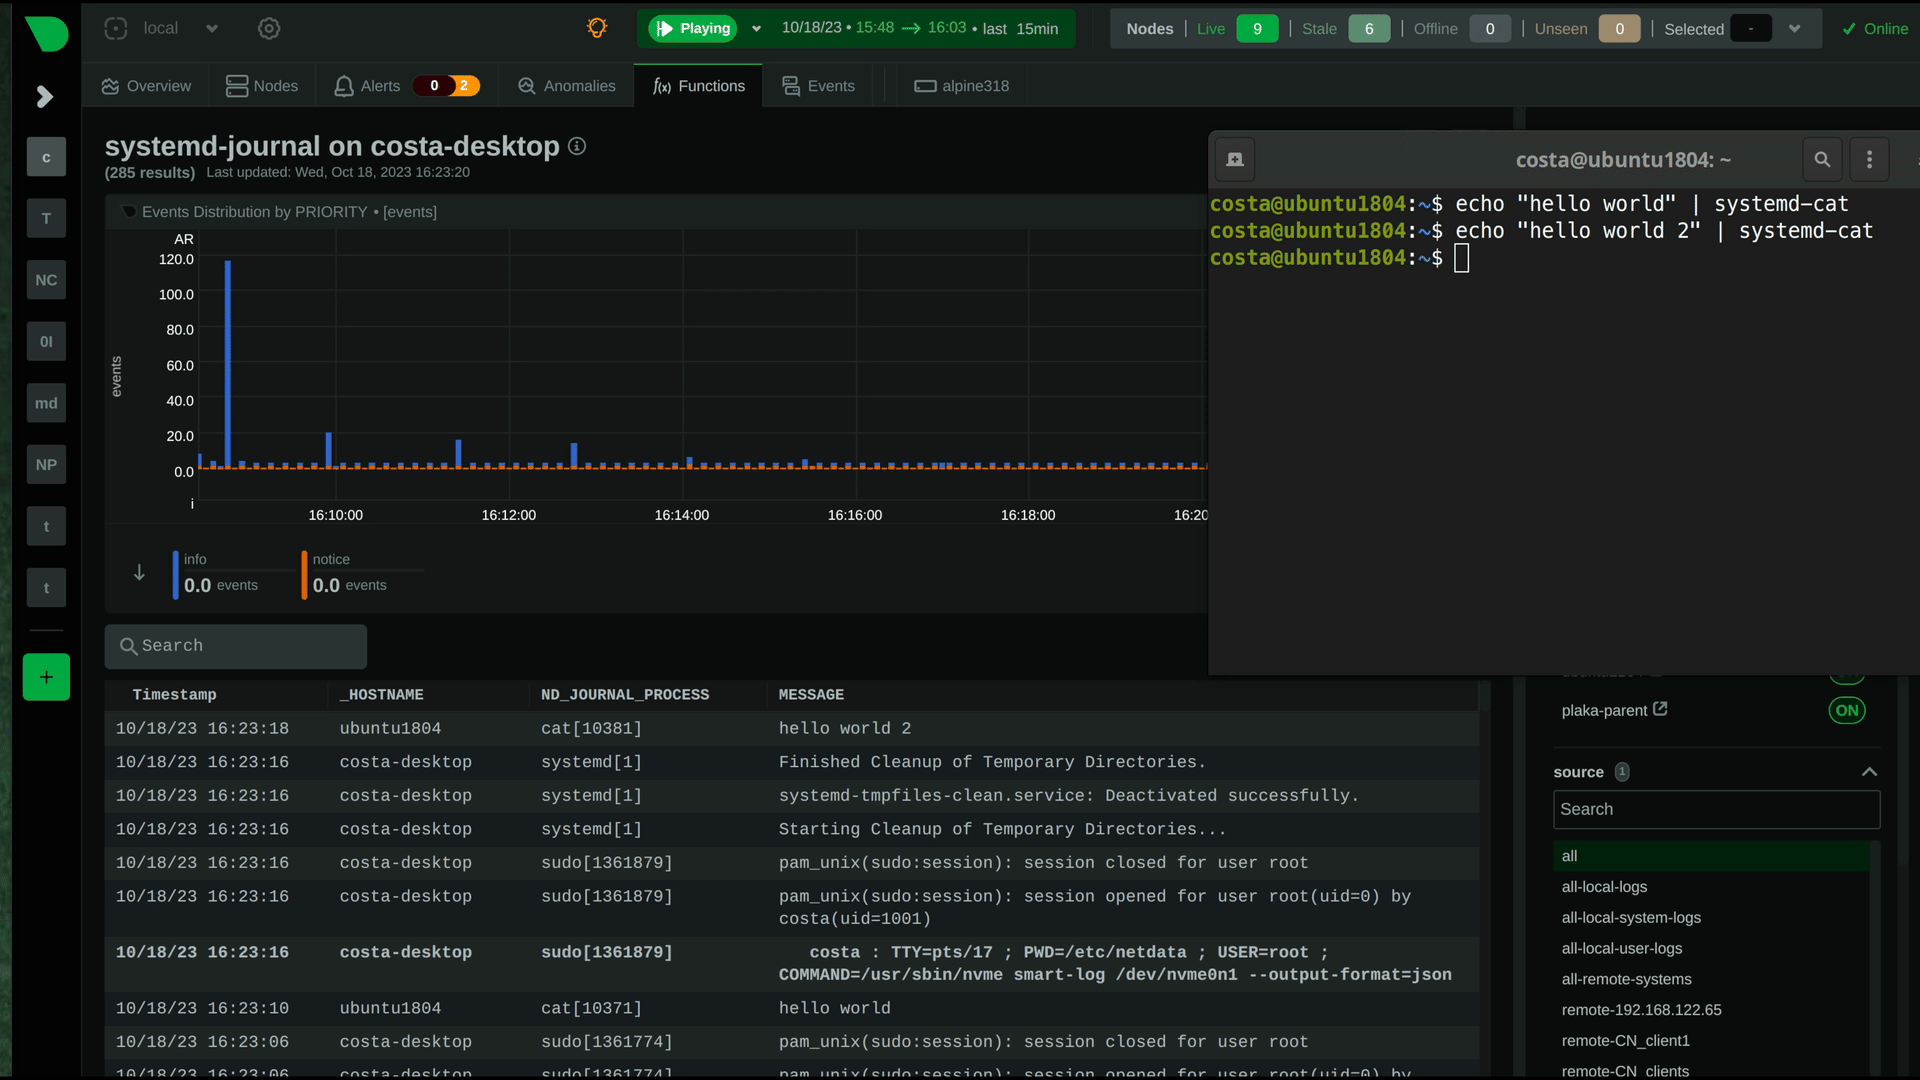
Here it is in action, in Netdata:
196
197